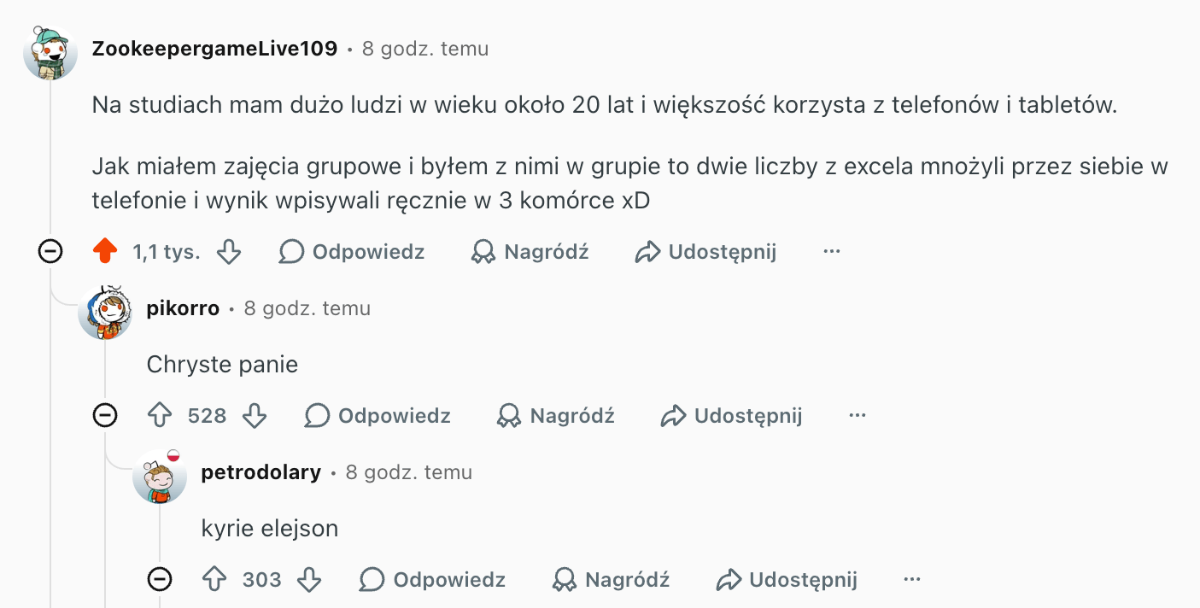
@Klockobar nie dziwi mnie. młodzi ludzie coraz częściej nie mają komputerów, bo telefon wystarcza im do wszystkiego. a jeśli człowiek nigdy nie korzystał z excela to nie dziwi mnie, że zna nawet podstawowych funkcjonalności.

@BoJaProszePaniMamTuPrimaSorta Miałem excela w szkole. Nienawidziłem tego gówna, nic z niego nie pamiętam.
@Alembik ja excela sam się nauczyłem na tyle, ile potrzebowałem. ale w tych czasach już nie potrzebuję tego skilla, bo dużo szybciej tematy ogarniają za mnie llmy.
To mi przypomniało historię na Erasmusie lata temu. Na wykładzie laska zwróciła się oburzona do wykładowcy, że wysłał pdf źle obrócony. I ona przy wszystkich kładzie lapka na boku, że teraz musi tego pdf tak czytać na lapku 😂 więc zawsze się ktoś znajdzie.

@Klockobar dostarczamy aplikacje do użycia wewnątrz korpo, boomerzy i zoomerzy mają dokładnie takie same problemy z obsługą. Przy czym ja jestem z tych co uważa, że aplikacja powinna być intuicyjna nawet jak wygląda jak gówno to ma działać, więc do każdej pierdoły się dowalam że jest źle opisane albo wykonane.
Zaloguj się aby komentować

Entity i Value Object to jedne z podstawowych building blocks taktycznego Domain-Driven Design. W artykule pokazuję, czym się różnią, jak wykorzystać je do pilnowania inwariantów oraz w jaki sposób można je wykorzystać, by ograniczyć problem Primitive...

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.13.md
Beyond Lazarus: Organization of DPRK cyber capabilities - https://www.sekoia.com/blog/beyond-lazarus-organization-of-dprk-cyber-capabilities
Dell BIOS Passwords: Weak XOR Encryption Allows Recovery from SPI Flash (CVE-2026-40639) - https://blog.amberwolf.com/blog/2026/july/dell-bios-passwords-weak-xor-encryption-allows-recovery-from-spi-flash-cve-2026-40639/
Testing race conditions with memory access tracing and stack-based delay injection - https://projectzero.google/2026/09/maccconc-race-condition.html
From P-Code to GNN: extract binary code semantics - https://blog.quarkslab.com/from-p-code-to-gnn-extract-binary-code-semantics.html
NetNTLMv1 Is Dead. Long Live NetNTLMv1 - https://www.outflank.nl/blog/2026/09/08/netntlmv1-is-dead-long-live-netntlmv1/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.11.md
Anatomy of SystemOptimizer - A BYOVD EDR Killer with a UAC Bypass - https://cham1ndux.github.io/posts/BYOVD-EDR-killer-with-a-UAC-bypass-and-a-lying-comment-block/
Privilege escalation from IIS AppPool to NT Authority/SYSTEM via AD CS RPC endpoint - https://www.mannulinux.org/2026/08/Privilege-escalation-from-IIS-AppPool-to-NT-AuthoritySYSTEM-via-AD-CS-RPC-endpoint.html
Dissecting a PHP web server rootkit - https://www.sophos.com/en-us/blog/dissecting-a-php-web-server-rootkit
Trust no one: are one-way trusts really one way? - https://offsec.almond.consulting/trust-no-one_are-one-way-trusts-really-one-way.html
AdaptixC2: Fingerprinting an Open-Source C2 Framework at Scale - https://censys.com/blog/adaptixc2-open-source-c2-framework
#informatyka
Zaloguj się aby komentować

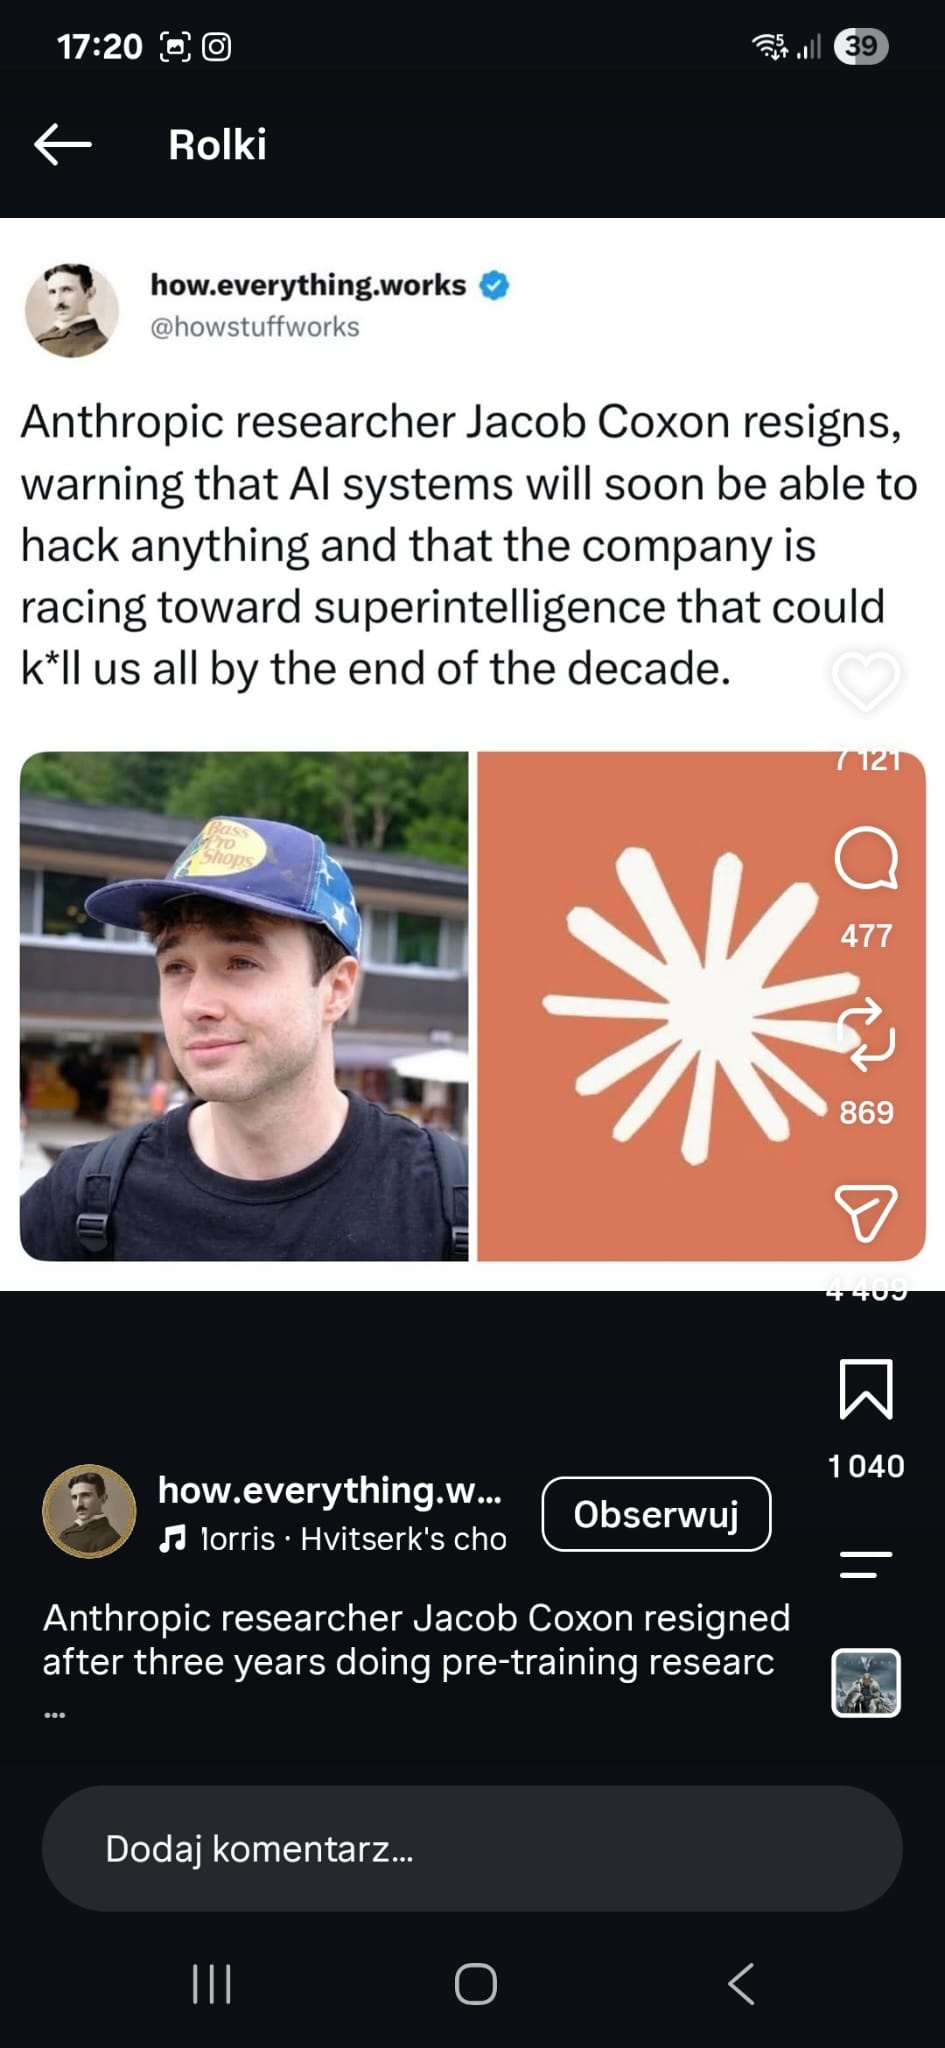
@inty Fast forward three months later - former Anthropic researcher creates his own AI start-up aiming to build AGI.

@inty niech anthropic i openai wejdą w końcu na giełdę, bo ile mozna czytać tego pierdolenia pod IPO
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.09.md
Can local open-weight LLMs detect vulnerabilities, or do they mostly just guess? - https://martinativadar.github.io/posts/llm-vulnerability-research.html
Why you Shouldn’t bypass MFA for your office IP adresses - https://ourcloudnetwork.com/why-you-shouldnt-bypass-mfa-for-your-office-ip-adresses/
DragonForce Ransomware Analysis: Inside a Verified Windows Locker - https://darkatlas.io/blog/dragonforce-ransomware-analysis-windows-locker
Token Theft in Microsoft Entra ID (Part 1 of 4): Threat Landscape and Attack Techniques - https://insinuator.net/2026/08/token-theft-in-microsoft-entra-id-part-1-of-4-threat-landscape-and-attack-techniques/
Attacking and Defending SCOM: Management Server Relay and Obtaining Run As Credentials - https://www.guidepointsecurity.com/blog/attacking-and-defending-scom/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.07.md
Awesome Large Language Models for Vulnerability Detection - https://github.com/huhusmang/Awesome-LLMs-for-Vulnerability-Detection
Peeling the Sentinel: A Market-Leading EDR Comes Apart With Undergraduate Tools - https://blog.nullze.net/posts/peeling-the-sentinel/
UAC Bypass - CMSTPLUA COM Exploitation - https://0xsec.gitbook.io/0xsec/windows/uac-bypass-cmstplua-com-exploitation
Something is jamming GPS over Europe. Here's what we found - https://www.youtube.com/watch?v=tz23G_UXCGA
Caught in the Octopus Trap: Unauthenticated RCE in Argo CD with CodeQL - https://www.synacktiv.com/en/publications/caught-in-the-octopus-trap-unauthenticated-rce-in-argo-cd-with-codeql
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.05.md
Threat Intelligence Report: University Leak Exposes Russia’s Military Cyber Training Pipeline - https://dti.domaintools.com/research/threat-intelligence-report-university-leak-exposes-russias-military-cyber-training-pipeline
Lost in relocation: analysis of a new loader distributing CASTLESTEALER - https://www.elastic.co/security-labs/threat-command/oxloader-malware-loader-infostealer
klist.exe Revisited: Internals and Further Use Cases - https://jakeotte.com/posts/klist-revisited.html
Bluetooth Low Energy Security Testing, Consolidated: Introducing Caeruleus - https://www.praetorian.com/blog/ble-testing-caeruleus/
Bypassing Conditional Access policies that have a resource exclusion - https://dirkjanm.io/bypassing-conditional-access-with-resource-exclusion/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.03.md
if you copied any of these popular StackOverflow encryption code snippets, then you coded it wrong - https://littlemaninmyhead.wordpress.com/2021/09/15/if-you-copied-any-of-these-popular-stackoverflow-encryption-code-snippets-then-you-did-it-wrong/
Vulnify: Giving Your Agents a CVE Brain - https://trustedsec.com/blog/vulnify-giving-your-agents-a-cve-brain
Cores in space: The core memory module from a 1980 Spacelab computer - https://www.righto.com/2026/08/spacelab-core-memory.html
Privilege escalation from IIS AppPool to NT Authority/SYSTEM via AD CS RPC endpoint - https://www.mannulinux.org/2026/08/Privilege-escalation-from-IIS-AppPool-to-NT-AuthoritySYSTEM-via-AD-CS-RPC-endpoint.html
The SID that wasn't there: bypassing KB5014754 to Domain Admin on a fully patched AD CS https://0xmaz.me/posts/certsrv-id-cmc-addExtensions-KB5014754-bypass/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.09.01.md
Jalapeño’s first results show industry-leading speed and efficiency in AI inference - https://openai.com/index/jalapeno-first-results/
VMs won't contain cyber-capable agents - https://blog.trailofbits.com/2026/08/26/vms-wont-contain-cyber-capable-agents/
Static Devirtualization of Tencent VM - https://aftermathlabs.net/blog/31/07/2026/
From P-Code to GNN: extract binary code semantics - https://blog.quarkslab.com/from-p-code-to-gnn-extract-binary-code-semantics.html
The Hugging Face incident and the road Ahead - https://openai.com/index/hugging-face-incident-and-the-road-ahead/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.30.md
Route of Root: Bring a "DoS only" bug to LPE and bypass the existing patch to win $10,500 in kernelCTF - https://nebusec.ai/research/cve-2026-43501-route-of-root/
Unmasking TeamPCP, King of Software Supply Chain Attacks - https://flare.io/learn/resources/blog/teampcp-software-supply-chain-attacks
Malware analysis: part 11. How to create your own mini-GPT for binarny analysis - https://cocomelonc.github.io/malware/2026/07/25/malware-analysis-11.html
Into the Dark - DarkSword Kernel Exploit Writeup - https://therealclarity.github.io/blog/clearsword/
The QTFY Hunt: How Chinese Hackers Were Tracked and How the Internet Became the Sensor - https://zerotracelab.com/blog/qtfy-hunt-internet-sensor
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.28.md
Two bytes to RCE: chaining rift + PoolSlip into an ASLR-independent nginx 1.30.0 exploit - https://blog.verichains.io/p/two-bytes-to-rce-chaining-rift-poolslip
Patterns and problems in emerging multiagent systems - https://www.anthropic.com/research/multiagent-systems
RoguePlanet: Defender Quarantine Pipeline LPE Zero-Day - https://www.offsitedark.com/signals/rogueplanet-defender-lpe-zero-day
Popping Microsoft’s Sandbox: Dataverse Security Risks in Plugin Containers - https://www.beyondtrust.com/blog/entry/dataverse-security-plugin-sandbox-risks
MmMapIoSpace Returns NULL: Tracing the Real Kernel Mechanism Through ntoskrnl - https://sibouzitoun.tech/articles/mmmapiospace-returns-null-tracing-the-real-kernel-mechanism-through-ntoskrnlexe/
#informatyka
Zaloguj się aby komentować
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.26.md
Awesome Vehicle Security - https://github.com/jaredthecoder/awesome-vehicle-security/
Static Devirtualization of Tencent VM - https://aftermathlabs.net/blog/31/07/2026/
The Bug Bounty Singularity: Our Hackbot - https://josephthacker.com/hacking/2026/07/01/we-built-a-hackbot.html
Local AI for Penetration Testing & Research - https://projectblack.io/blog/local-ai-for-cyber-security/
Client Connector App Release Summary (2026) - https://help.zscaler.com/zscaler-client-connector/client-connector-app-release-summary-2026
#informatyka
Zaloguj się aby komentować
AI jest wykorzystywana zarówno przez zespoły deweloperów i architektów jak również przez biznes i ekspertów domenowych. Sprawia to, że język wszędobylski (Ubiquitous Language) zyskuje jeszcze większe znaczenie i wartość w codziennej pracy. Ubiquitous Language to wspólny język domenowy, który...
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.24.md
The QNAP Pattern - https://runiclabs.io/research/qnap-architecture/
SynkLoader: when you throw in everything but the kitchen sink - https://expel.com/blog/synkloader-when-you-throw-in-everything-but-the-kitchen-sink/
When Defenses Become Attack Surface: CVE-2026-20971, a Samsung Kernel UAF - https://lucidbitlabs.com/blog/when-defenses-become-attack-surface/
Fantastic clear-text passwords and where to collect them (Part 2 - Windows) - https://dfir.ch/posts/fantastic_passwords_windows/
CrystalPotato - GodPotato in Crystal - https://ricardojoserf.github.io/crystalpotato/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.22.md
Vulnerability and malware checks in uv - https://astral.sh/blog/uv-audit
Managing the cyber risk of agentic AI - https://www.ncsc.gov.uk/blogs/managing-the-cyber-risk-of-agentic-ai
Reading an offline ntds.dit with one binary - https://zaferbalkan.com/ditjson/
I found a KVM guest-to-host heap corruption bug and someone else got there first - https://blog.himanshuanand.com/2026/08/i-found-a-kvm-guest-to-host-heap-corruption-bug-and-someone-else-got-there-first/
SakDriver: Reversing a Kernel Driver Rootkit - https://0xsec.gitbook.io/0xsec/malware-analysis/sakdriver-reversing-a-kernel-driver-rootkit
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.20.md
IonStack part II: GhostLock, a stack-UAF that has existed in ALL Linux distributions for 15 years - https://nebusec.ai/research/ionstack-part-2/
Reverse engineering what HyperGuard monitors in ntoskrnl - https://fluxsec.red/what-does-hyperguard-skpg-monitor-vtl1-windows-internals-secure-kernel-patch-guard
WS-Trust Autologon Endpoint: Password Spray Without Smart Lockout Blocking - https://www.varonis.com/blog/ws-trust-autologon-endpoint
IDT Table Hijacking under VBS/HVCI/kCET in Windows 11 - https://www.exploitpack.com/blogs/news/idt-table-hijacking-under-vbs-hvci-kcet-in-windows-11
Defenders Arise: Examining 7Zip data extraction with Registry analysis - https://thinkdfir.com/2026/08/18/defenders-arise-analysing-7zip-data-extraction-with-registry-analysis/
#informatyka
Zaloguj się aby komentować
Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.18.md
TAPOcalypse Now: Exploiting TP-Link Smart Devices From Anywhere - https://labs.taszk.io/articles/post/tapocalypse/
Smile, You’re on Camera. Part 2: Hiring Lazarus APT’s IT Workers in a Fake DeFi Startup - any.run/cybersecurity-blog/lazarus-group-it-workers-investigation-part-two/
Modern implant design: position independent malware development - https://5pider.net/blog/2024/01/27/modern-shellcode-implant-design/
Mitigated API authentication bypass for python.org download metadata - https://pyfound.blogspot.com/2026/06/mitigated-api-bypass-for-download-metadata-python-dot-org.html
Windows 11 Hibernation on ARM64: the Boot Manager, winresume, and the hiberfil.sys Format - https://www.msuiche.com/posts/windows-11-arm64-hibernation/
#informatyka
Zaloguj się aby komentować
Qurua, zaćmienie jakieś.
Macie działający patent na szybkie pobranie filmu z jutuba?
Gugel wyświetla jakoś szajs.
#zalesie #gownowpis #informatyka
Zaloguj się aby komentować